
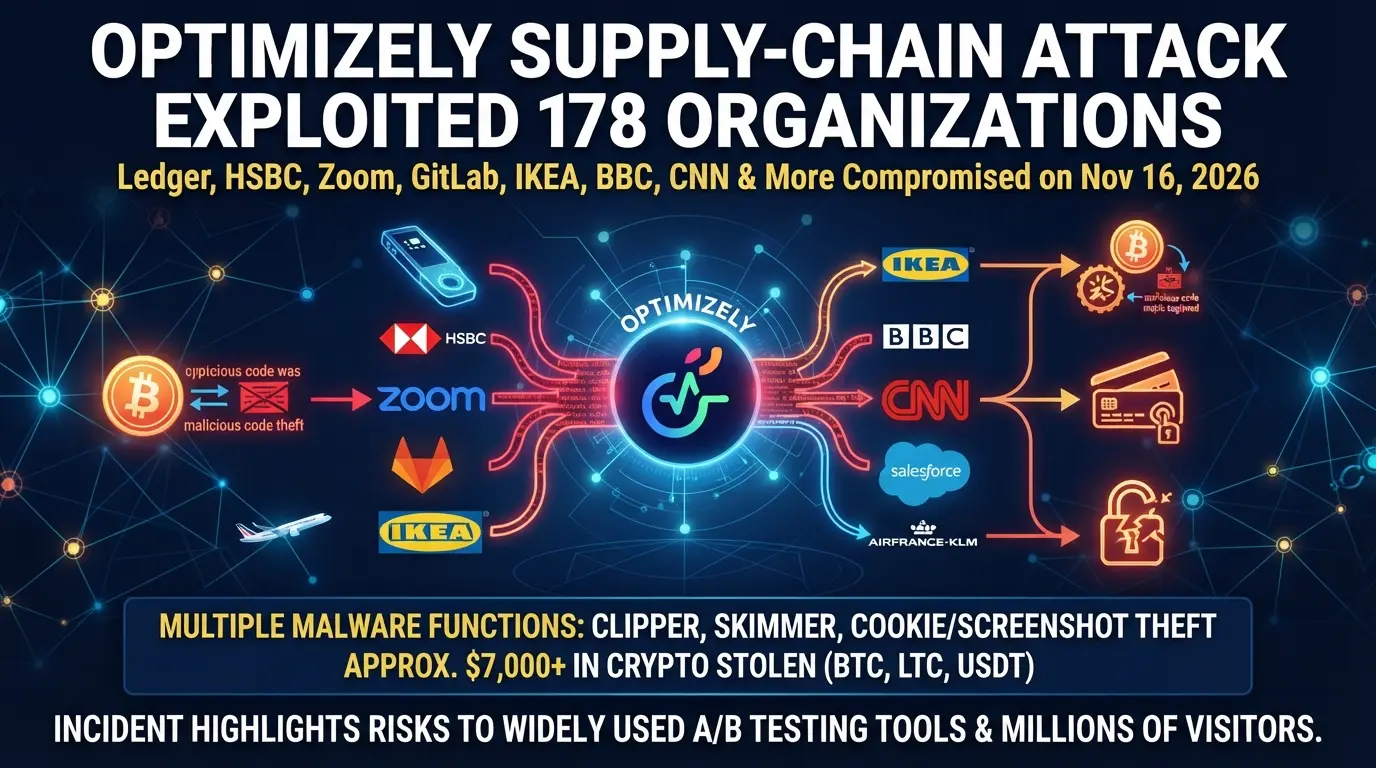
A supply-chain attack exploited a vulnerability in Optimizely’s web experimentation platform and injected malicious code into the websites of at least 178 organizations on November 16, 2026. Among those affected are hardware wallet maker Ledger, bank HSBC, Zoom, the BBC, CNN, Salesforce, GitLab, IKEA, Equifax, and Air France-KLM, among others.
Optimizely confirmed the incident. An unauthorized attacker exploited a flaw in the Experimentation account signup flow to insert malicious JavaScript into customer projects. Because Optimizely’s scripts are automatically loaded by visitors’ browsers from the company’s own servers, the malware was distributed without the brands’ own websites needing to be directly compromised.
How the malware worked
The code was a multi-purpose kit. Its main cryptocurrency-related function was to act as a “clipper” (address swapper):
It identified valid Bitcoin, Ethereum (and EVM networks), Solana, Tron, TON, Litecoin, Bitcoin Cash, and Dogecoin addresses on the pages.
It replaced those addresses with wallets controlled by the attacker, both in the page content and in what the user copied to the clipboard.
Anyone who copied a legitimate address while an infected page was open could unknowingly paste the attacker’s address and send funds to it.
In addition, the malware included a credit-card skimmer (capturing numbers, expiry dates, and CVVs entered into the site’s own forms), cookie and screenshot theft, and attempts to deliver exploit kits to older iPhones and iPads.
Impact and amounts stolen
Security firm Report URI, which identified the attack, analyzed 1,611 Optimizely snippets and found malicious code in 188 of them, belonging to 178 organizations. The financial and banking sector was the hardest hit (around 32 entities), followed by technology, media, and some crypto and trading companies (including Ledger).Wallets linked to the attacker received approximately $7,000 to $7,150 in cryptocurrency (mainly Bitcoin, Litecoin, and USDT) on the day of the attack. Part of that amount was moved quickly. There are no precise estimates of how many credit cards were compromised or how many iOS devices were affected.
Optimizely’s response
The company blocked the vulnerability, removed the injected code, secured the affected accounts, and contacted customers. In a statement, it said: “The vulnerable path is blocked, the injected code was removed, and customers have been contacted directly.” Cleanup of the snippets took place throughout November 16, and by late that night the majority had been cleaned.
Recommendations
Experts advise anyone who visited potentially affected sites on November 16 to carefully check any cryptocurrency transfers made after the visit, confirming that the destination address was the one intended. It is also recommended to monitor credit-card statements and use up-to-date security tools.The incident highlights the risks of supply-chain attacks on widely used tools for A/B testing and website personalization. Although the volume of cryptocurrency stolen was relatively low compared with other recent hacks, the scale of high-traffic sites involved raises concern about the exposure of millions of visitors






