
Introduction
For more than 2 decades since the publication of Satoshi Nakamoto's white paper "A peer to peer electronic cash system" back in 2008, Bitcoin’s cryptographic foundation has stood strong against hackers, national governments and and central banking authorities who tried to question its decentralised technology. At the same time Quantum computing has emerged as one of the most powerful technological shifts of the 21st century promising to revolutionize every aspect of global economy from medicine research, logistics, engineering, physics and of course Information Technology. And the capability of quantum machines to solve complex mathematical problems such as the classical cryptographic algorithms, can label it as a real threat to Bitcoin technology with the results being catastrophic for the entire crypto ecosystem. If Bitcoin, the pioneer cryptocurrency may be break, the rest of the altcoins soon or later will also follow.
In one of his interviews on Youtube, CryptoCapitalist a Greek crypto Youtuber, hosted Christian Papathanasiou a cybersecurity expert and Bitcoin enthusiast to talk exactly about this. Quantum Bitcoin is a REAL threat to Bitcoin!
For those who can understand Greek, here you can find the complete interview session :
Who is Christian Papathanasiou
According to his Linkedin Profile, Christian Papathanasiou is a Bitcoin Enthusiast and a notable Cybersecurity Expert with more than 20 years experience as a Penetration Tester for multinational banking Institutions such as Citibank or the Royal Bank of Scotland. His research in cybersecurity has been presented in notable magazines such as Forbes, and Reuters and he has been a major presenter in cybersecurity conferences such as the Black Hat and the DEF CON. He has also contributed in the development of the security guidelines of the European Organisation for the Network Security and Informatics (ENISA) for the safe development of mobile apps. He is also a founding member of the UK Digital Currency Association and an early adopter of the Bitcoin community.
Interestingly, during his interview he mentions that he discovered Bitcoin after reading a risk report of the banking institution he was employed where Bitcoin was described actually as a potential threat against his employer establishment. Yet, Christian was seduced from the Bitcoin Technology and after reading Satoshi Nakamoto' White Paper, he started searching for any information possible on the web about Bitcoin. After the fall of Mt.Gox, he decided to develop his own Bitcoin trading platform! However although he was initially cleared for a commercial use of his platform, he was later denied a business banking account from HSBC to run his business, so he quit his ambitious project.
Quantum Computing is a Real Threat to Bitcoin
Bitcoin's security depends on cryptography that classical computers cannot break, as finding a private key would take longer than the age of the universe. This allows users to trust mathematical laws for non-custodial asset security without third parties, assuming proper security practices.
In fact, Bitcoin cryptography technology is divided in 2 parts. One technology is SHA-256 which is used for the construct the Bitcoin Blocks (hashing). The other part is the ECDSA (Elliptic Curve Digital Signature Algorithm) key which is a cryptographic pair of a private and a public key - both used to sign and verify digital data securely using elliptic curve mathematics. CDSA algorithm can be in fact solved with the Shor's Algorithm. But today this is not possible to happen without a revolutionary powerful computer system which hasn't been invented yet.
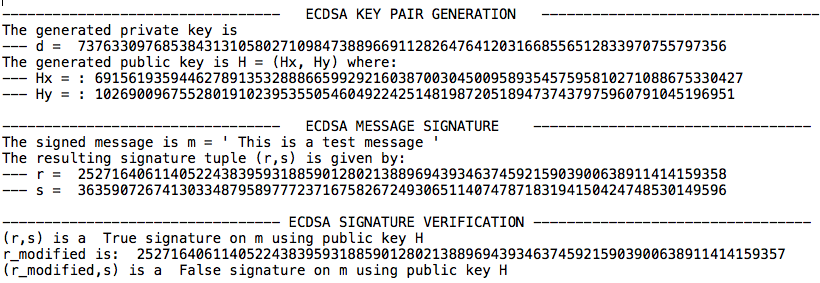
Christian Papathanasiou believes that the SHA-256 technology isn't the part of Bitcoin on risk against Quantum Computers, but the real threat lies on ECDS mechanism. However, according to several IT Scientists and Researchers, by 2030 Quantum Computing major players such as IBM and Google will be able to scale quantum processor power enough to break the ECDS mechanism of Bitcoin by making use of the Shor's Algorithm, transferring as a consequence the threat to the Bitcoin wallets by exposing the private keys of the users.
In my article back in November 2022 with title "Food, drinks, chain-analysis and post-quantum crypto at The LAB!" I mentioned the presentation of Dr. Mark Webber who tried to explore the vulnerabilities of the bitcoin blockchain due to the development of the quantum computing.
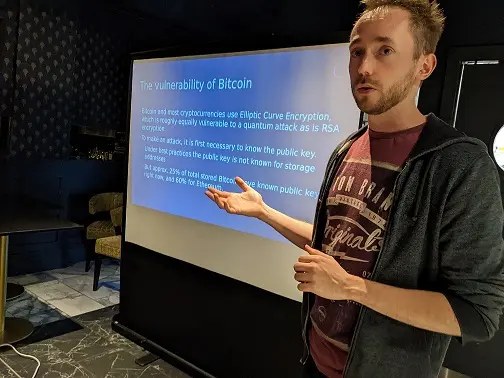
Reports from global financial institutions have also estimated the financial damage caused by a post-quantum Bitcoin "hack". A 2022 Hudson Institute study warned that a quantum hack could cause several of trillion of dollars in losses and in 2025, Deloitte emphasized that about 6.2 bitcoin in circulation are at risk because their public keys may be exposed. At the same time, governments, researchers and crypto enthusiasts such as Christian Papathanasiou have begun pushing for a post-quantum cryptography standard.
And Q-Day has been anticipated as the future date when quantum computers will be able to gain for real the capability to break the classical cryptographic algorithms in which Bitcoin security is relied.
Granny's House
In a simple words, Papathanasiou reckons that our granny's house in the village that still has an old locker with a big cast iron key at the door where the keyhole for the key is massive and anyone might put his eye on the hole to take a sneak of what's behind. For the 1920s when the lock was designed, it was believed to be safe and not replicable. and the door might have stayed safe for several decades. Yet, as technology evolved, intruders were able to replicate these keys. so what the owners of the house did. They did kept the same old door but the initial lock was changed to a safer design so nobody could replicate them and none could even see what's behind the door.
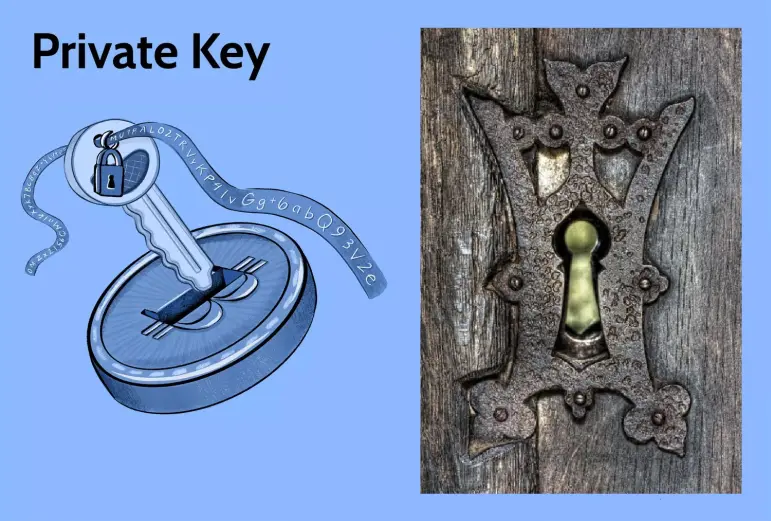
If we take the same analogy to the Bitcoin, when Bitcoin was designed back in 2008 by Satoshi Nakamoto, it was designed with best possible cryptography technology available in the late 00s hoping that it is safe for the next 20-30 years of cryptography and computing evolution.
In a relevant question on Bitcoin Talk back in 2010, Satoshi Nakamoto also mentioned that
if the hash breakdown came gradually, we could transition to a new hash in an orderly way
So due to the latest developments in Quantum computing and Artificial Technology, it is mandatory to change the "lock" of Bitcoin and upgrade it against the modern risks.
The antidote to the Threat
Nevertheless, panic is NOT an option. Neither it is an option to sell all of your Bitcoin because of the quantum threat. Christian remembers that 30 years ago, the Y2K threat of the IT systems put all the world in panic. When clocks of the modern computer synchronisation systems were designed in 70s and 80s, nobody could predict the popularity of Information Technology systems and how much would influence our everyday life. So when the year 2000 was approaching, everybody feared that it would be the end of our civilisation and a massive effort took place from IT Engineers to avoid any loss of synchronisation between them. In the end, in the 2000 new years eve nothing happened and life continued as usual.
He also notes that it isn't only Bitcoin that it is in threat of the Quantum Bitcoin but every single cryptography system from world wide web's SSL certificate to banking security algorithms are also threat and that all the major banking institutions are already trying to upgrade their system for the post-quantum era.
Specifically for the Bitcoin, Bitcoin Foundation has already established several working groups working groups working on the Bitcoin Quantum threat..
A proposed Bitcoin soft fork designed to protect the network against long-exposure quantum computing attacks is known as Bitcoin Improvement Proposal (BIP) 360 proposal and it was co-authored by Hunter Beast, Ethan Heilman, and Isabel Foxen Duke. Bitcoin Improvement Proposal (BIP) 360 is also known as Pay-to-Merkle-Root (P2MR).
Another proposed Bitcoin soft fork is known as Bitcoin Improvement Proposal (BIP) 361. BIP361 has similar functionality to BIP360 and it has been mianly co-authored by Christian Papathanasiou and Jameson Lopp a Cypherpunk and Angel Investor on April 2026. If there is a consensus about the Bitcoin Improvement Proposal (BIP) 361 between miners, Bitcoin developers and users and all Bitcoin stakeholders, it will result to the qBTC through a soft fork, a quantum-safe Bitcoin sidechain. And Christian Papathanasiou describes Bitcoin Improvement Proposal (BIP) 361 as an open-heart operation since it will change the whole cryptography architecture of the Bitcoin Core algorithm not just the Block size as it happened in the past resulting to Bitcoin Cash hard fork.
However, there is already a huge controversy over the dominant Bitcoin Improvement Proposal. BIP 360 suggests that if after the upgrade an individual manages to break the private keys of Satoshi Nakamoto's wallet, he deserves all Satoshi Nakamoto's coins as long as the Bitcoin Core code allows that. But in that scenario, Christian Papathanasiou claims when these Bitcoins will get exchanged in a crypto exchange for FIAT money, then Bitcoin's price will get reduced by 99.9999% instantly.
In Bitcoin Improvement Proposal (BIP) 361, Christian Papathanasiou and his team focus to provide more protection to Satoshi Nakamoto's wallet by implementing the quantum upgrade in 3 phases within 5 years providing to wallet owners a migration path from pre-quantum addresses to post-quantum addresses. In the case of custodial wallets i.e. when the users are keeping their Bitcoins in a crypto-exchange, just like it happened to the previous Bitcoin forks, the crypto exchanges will execute the post-quantum fork automatically providing the relevant post quantum coins to the owners automatically. In comparison with BIP 360, "Lost Wallets", just like it happens with Satoshi Nakamoto's wallet or with deceased owners, or with lost key wallets, the migration will take place after the 5 year period to avoid having someone hacking these wallets including Satoshi Nakamoto's wallet. But for this 5-years migration period these coins will be locked or frozen because nobody would be able to interact with non Quantum ready Bitcoin addresses. Christian Papathanasiou has estimated that the total amount of Bitcoins at risk is 6.2 millions Bitcoins and he also mentions that even the most famous Bitcoin ETF providers such as BlackRock have informed their customers (as they are obliged to do so) that they commit to a Post-Quantum Bitcoin upgrade.
Finally, Christian Papathanasiou worries mostly that the whole process of having a BIP implemented into Bitcoin core is too slow and it takes a lot of time even if there is a consensus about the BIP. And from the other hand, there is less than 5 years for the Q-Day. Therefore, Christian Papathanasiou offers already a post-quantum ready Bitcoin sidechain where Bitcoins are being wrapped in Quantum Wrapped Bitcoins.
And this is where CryptoCapitalist disagrees with the Quantum Wrapped Bitcoins because he believes that he loses the ownership and the custody of his Bitcoins through a smart contract. Christian Papathanasiou replies that his team have developed a distributed system called "Samir Secret Cherry" where the private key is being cut in 1000 pieces and distributed in 1000 separate nodes that doesn't allow to noone to move the Quantum Wrapped Bitcoins.
AltCoins Resistance
Unfortunately, Bitcoin faces the hardest challenge of the quantum threat because of its
decentralized and conservative upgrade path. Yet, several cryptographic-oriented altcoins such as IOTA, Nervos, Algorand, and Cardano, only because they were designed and develloped AFTER Bitcoin, they have already taken into consideration by default the post-quantum threat, demonstrating different strategies for building their quantum resistance today.
According to CryptoBriefing, just recently on October 2026, Starknet community of more than 3.200 wallets has voted to explore becoming an independent layer 1 blockchain designed to withstand quantum-computing threats. A 93.5% of votes also supported further research led by StarkWare and the Starknet Foundation in a non-binding community poll with a draft white paper being published on November 2026.
Final Thoughts
Nevertheless, the quantum threat to Bitcoin is not science fiction. It is a real threat!
For those who have studied and work close to technology, they know very well that technology never stays stable but it evolves constantly. And for those who choose to close their eyes to Quantum Threat, time soon will arrive for the moment Satoshi Nakamoto foresaw in the future where Bitcoin should transition to a new hash in an orderly way...
Disclaimer: All information found on this article is for informational purposes only. I do not provide any personal investment advice so please make your own research before proceeding to any investment/trading actions
Publish0x Blockchain stories on [Crypto-monkey] (https://www.publish0x.com/crypto-monkey)
My Censored Blockchain stories on [Read.Cash](https://read.cash/@feax21)
Follow me on [Medium](https://medium.com/@feax21)
Follow me on [X](https://twitter.com/feax31)
Follow me on [Facebook](https://www.facebook.com/profile.php?id=61572425464725) ***NEW ACCOUNT***
Follow my [cryptoblog](https://cryptomonkey.weebly.com/)
Follow my [blogspot](https://monkey2crypto.blogspot.com/)
Follow my [Cryptomonkey Jotform App](https://eu.jotform.com/app/cryptomonkey/cryptomonkey)
NFT & $WAX donations at [n4gay.wam]






