Yesterday, in addition to Polymarket (which suffered a frontend attack), Binance was also hacked (over $6.3 billion), but I've read a lot of confusion about Tether and Circle freezing. It's well known that these two companies are centralized: they have the "button" to freeze assets remotely. They're not selling you a decentralized product. USDT, USDC, EURC, PAXG, XAUT, USDP, etc. can all be frozen remotely. In your opinion, is it right or wrong to freeze funds? Today you're doing it because there's been a hack (a noble reason); tomorrow they might do it at the request of a government.
In any case, the distinction is:
1) Smart contract censorship (USDC, USDT, EURC).
2) Censorship at the consensus/validator/chain level (which, for example, happened on Arbitrum and happens on all layer 2 platforms with a centralized sequencer).
This isn't a matter of centralized DeFi. Yesterday, what always happens during major hacks happened: Tether and Circle froze funds. This is well known. It's not a surprise. These two stablecoins are very different from DAI. Censorship of DAI can't happen at the smart contract level (like USDC and USDT) but must happen at the chain consensus level (validators, forks, etc.), so it's much more difficult.
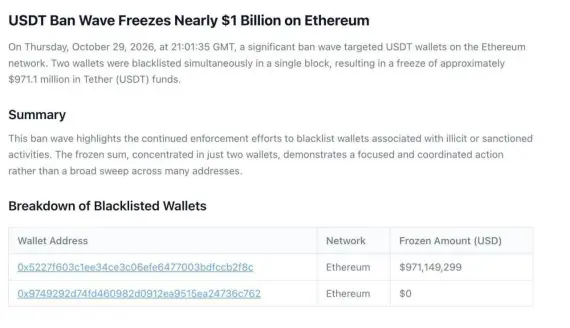
Other inaccuracies I've read concern Aave. The attacker deposited USDT BEFORE the freezing. Frozen USDT cannot be transferred or deposited to borrow assets. "Why did Aave freeze deposits and borrows?". To prevent him from depositing more collateral and taking more ETH (which can't be frozen). Since the USDT were deposited BEFORE the freezing (not in Aave's smart contract), they are normally liquidable by Aave. If ETH drops in price, the collateral (USDT) would be sold. Technically, there is no bad debit.
What is known about the hackers?
1) They likely belong to North Korea (Lazarus Group/TraderTraitor).
2) It appears to have been an attack on the Binance hot wallet signing infrastructure, using EIP-7702 and pre-arranged authorizations. The wallet used to fund the operations was powered by Tornado Cash.
3) The attacker distributed the funds across numerous wallets and quickly converted the most easily frozen assets (if you steal USDC or USDT, you know you need to convert them quickly, switching from Ethereum to Monero or Bitcoin).
4) $2.7 billion was frozen from Tether, Circle, Paxos, Ripple, First Digital + $ETH and $ARB by the Arbitrum Security Council.
And the unfrozen funds? He converted a huge amount of stablecoins and other tokens into ETH through:
- Uniswap and UniswapX.
- 1inch Fusion.
- Other AMMs.
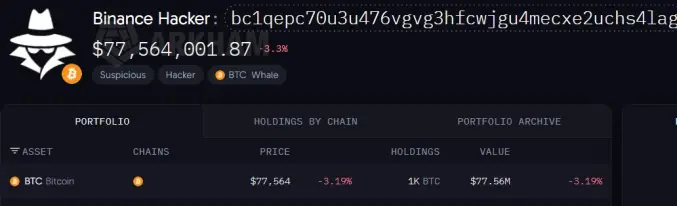
18,270 BTC were distributed to 19 addresses.
One wallet held approximately 638.2 million TRX. A second wallet, with approximately 44.5 million, began distributing small amounts to new addresses.
970,549 SOL appear to be sitting in the wallet; another portion (unconfirmed) appears to have been laundered with the memecoin launch.
Address of the attackers:
0x5227f603c1ee34ce3c06efe6477003bdfccb2f8c (Main receiver, frozen stablecoins, ETH and other tokens)
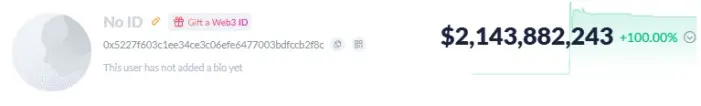
0xa97bf7836f8a08f9ed91d41453d371493fae8d10 (Second receiver, ETH and residual tokens)
0x8532fa14acaf483729c449b8458aeddb900543d4 197,460 ETH
0xc887af690e0301cd4edbbce8f8d31b4ec65b286a 137.602 ETH
0x897c80d1a9729e94460e2bd93178bd5215158df3 78.415 ETH
0x54401f80da97893a15d43566184635b6674bc942 32.954 ETH
For BTC:
bc1q0mtc2f5agpkvlq6hhahmfr3hlr55kyfjhl2mnm (initial address, then split into 19 addresses containing 1,000 BTC).
bc1qxrxujwxfnvz040jw76d26zhjdg5jura7hs968s (1,000 BTC).
bc1qepc70u3u476vgvg3hfcwjgu4mecxe2uchs4lag (1000 BTC).
bc1qdfhmlrdvg4tm87zjl0vyf0xflp5ql50q3g88gw (1000 BTC).
...
For TRON:
TSpe5HC3PRD2svJcr1YoGszhHk2mtkyZ8A (first recipient).
TRBdWqHnDVSZCVGfgHdKFLQPirQcA2PRki (wallet that fragmented the funds).
For SOLANA:
AffzFDKZbyMiU11zmVBoAqD25ugpr7xoWWyRyGigBEaU (970,554 SOL).
What will the hackers do? Such large sums are not easy to liquidate, though North Korean hackers typically do not compromise. It is strange, however, that they have not yet used mixers or transferred the funds into Monero. This could even mean returning the funds in exchange for a clean percentage.
Article always updated with all the possibilities of on-chain farming (airdrop): Some Sites To Earn Crypto Bonus (Old & New)