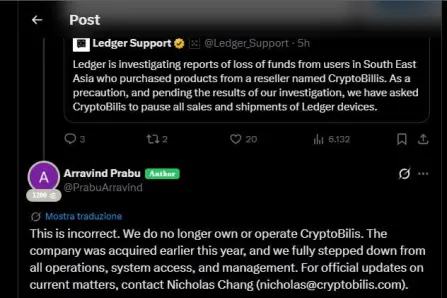
On October 9, users saw funds drained from their Ledger hardware wallets due to devices that were compromised at the source, likely containing embedded spyware. This attack affected devices purchased within the last three months in Southeast Asia from the third-party retailer Cryptobilis (which, so they say, were bought by a scammer).
In this article, I will outline some of the most common techniques for avoiding these scams and identifying counterfeit hardware wallets.
PRE-GENERATED SEED PHRASE
The device arrives with a seed phrase already generated and known to the scammer. The victim deposits funds believing the wallet is exclusively theirs, while the attacker already possesses the keys.
COMPROMISED HARDWARE AND ADDED COMPONENTS
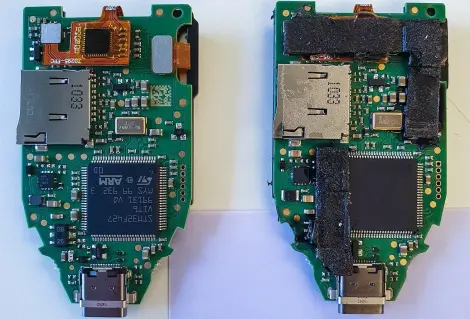
An apparently authentic device may contain unauthorized components, circuit modifications, or hidden communication interfaces. This allows for the interception of sensitive data or the exploitation of device vulnerabilities. It appears that OLED screens equipped with LTE modems and eSIMs are sometimes used to transmit data. Sometimes, a USB drive is simply attached to the Ledger device itself to spread malware.
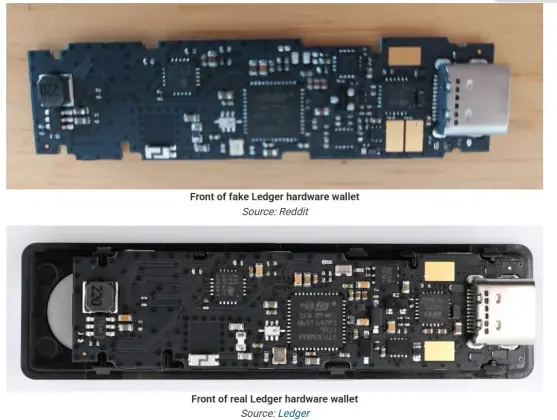
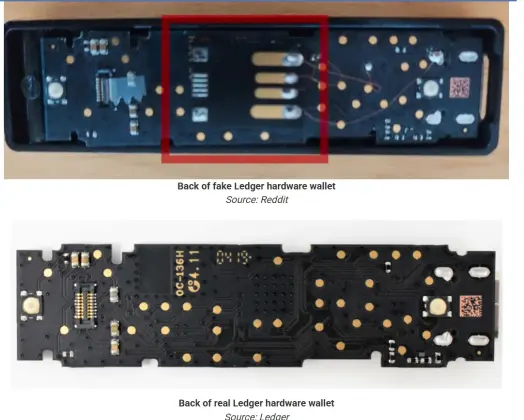
The photo below shows a Trezor that has been modified with unauthorized components.
FAKE DEVICE WITH MALWARE
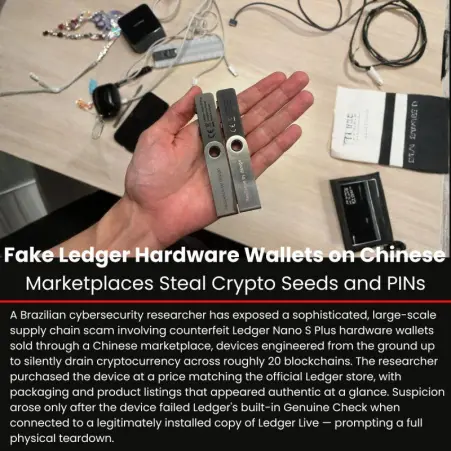
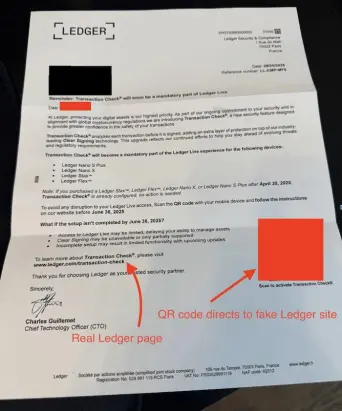
Scammers frequently send fake devices, complete with deceptive packaging and letters, containing malware. Victims are persuaded to switch to the new device under the guise of updates or enhanced security.
USED OR REFURBISHED DEVICES SOLD AS NEW
The seller initializes the wallet, retains the seed phrase, and delivers the device along with that seed. Even if the packaging appears legitimate, the previous owner can spend the funds at any time. This is a well-documented scam.
FAKE UPDATES AND CLONED WALLET APPLICATIONS
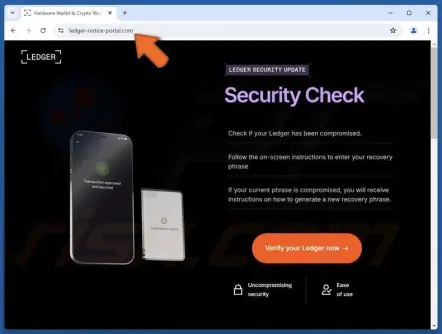
An app or website imitating, for instance, Ledger Wallet/Ledger Live displays a fake error, a synchronization request, or a mandatory update, prompting the user to enter their 24-word recovery phrase. The seed is then transmitted directly to the scammer.
FAKE TECHNICAL SUPPORT AND RECOVERY SCAMS
Social media accounts, Telegram profiles, or support websites impersonate the manufacturer, promising to resolve an issue or recover stolen funds, while asking for the seed phrase, a QR code scan, or remote access to the computer. Trust in the supposed support agent replaces technical vulnerability as the attack vector.
INFOSTEALERS, KEYLOGGERS, AND COMPUTER MALWARE
A keylogger records keystrokes, reads clipboard data and files, or intercepts data saved by software wallets. It can steal a seed phrase entered on the computer but generally cannot directly read the protected memory of a properly designed hardware wallet. The risk increases when the user types the phrase on a PC or smartphone.
LOW-ENTROPY SEED (RNG VULNERABILITY)
In this scenario, the device itself may be authentic, but a flaw in the random number generator makes keys predictable or drastically reduces the pool of possible seeds. A notable precedent is the Trust Wallet extension vulnerability discovered in 2022; a seed generation issue affecting certain Coldcard Mk3 versions was also reported in 2026.
MALICIOUS FIRMWARE
Malicious firmware, a compromised supply chain, or an inauthentic update can alter the wallet's behavior. The actual risk depends on the architecture; this does not mean that just any update can automatically extract a seed phrase from any hardware wallet.
MALICIOUS SIGNING AND BLIND SIGNING
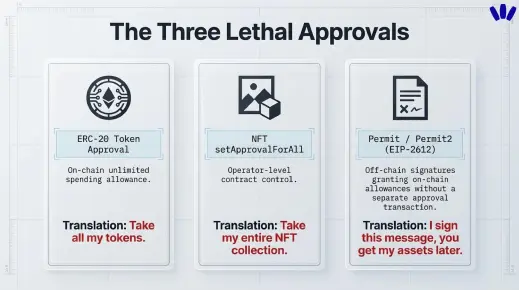
The victim approves a seemingly harmless transaction but actually signs a dangerous transfer or authorization—such as an unlimited ERC-20 approval or a "Permit". The seed phrase remains secret; it is the user-authorized signature itself that enables the theft.
SOFTWARE SUPPLY CHAIN ATTACKS
On December 14, 2023, an attacker compromised the Ledger Connect Kit package by exploiting a former employee's access, which had been obtained via phishing. dApps loading the malicious code could present transactions designed to drain wallets.
CLIPBOARD HIJACKERS AND ADDRESS REPLACEMENT
Malware modifies the address copied to the clipboard, replacing it with the attacker's address. If the victim fails to verify the full address before sending, they transfer funds directly to the attacker. The seed phrase is not exposed.
QR CODES AND FAKE RECOVERY INSTRUCTIONS
Tampered labels, QR codes, or manuals can redirect users to a fake setup site, a cloned application, or a deposit address controlled by the scammer. This is a variant of the supply chain scam that exploits the appearance of official documentation.
SIDE-CHANNEL ATTACKS AND KEY EXTRACTION
With physical access to the device, an attacker can exploit electronic vulnerabilities, power consumption analysis, fault injection, or flaws in memory protection. In 2019, Ledger Donjon documented a key extraction attack affecting Trezor One, Trezor T, KeepKey, and related devices.
Article always updated with all the possibilities of on-chain farming (airdrop): Some Sites To Earn Crypto Bonus (Old & New)