After my first review of some security keys back in 2020, today, five years later I now have some updated thoughts about those keys, their uses, and my current perspective on them.
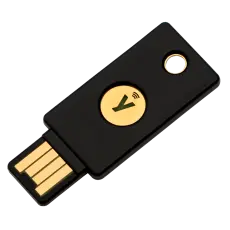
Security keys remain an excellent way to strengthen digital security, whether as a two-factor authentication (2FA) method or even as a primary authentication method. I use them with every online service that allows registration. Unfortunately, adoption of the FIDO login method has not grown as much as I expected since then.
However, some keys go beyond simple login — they can also be used for file encryption.
My main use of the YubiKey 5 Series nowadays is encryption. Since it relies on asymmetric cryptography, its main drawback is poor performance with large files. Unlike symmetric cryptography, which is optimized for productivity and speed, asymmetric encryption is better suited for smaller, individual items. For example, I use it to encrypt single files, such as TOTP backup codes from online services (stored in text files) and certain important documents.
For encryption, since my Yubikeys are all configured to generate and store the cryptography keys internally, I've no access to it (for better security), I always encrypt each file with at least 3 different Yubikeys, so in case on Yubikey get broken, lost or stolen, I do still can have access to all my encrypted files.