- “The logs looked clean. The alerts were green. But the breach was already 3 days old.”
I’ve seen this happen more times than I can count — teams with all the right tools (SIEM, EDR, firewalls, SOAR)… yet the attacker was already inside.
In this article, I break down why security operations centers (SOCs) still miss early signs of compromise — even with advanced tooling — and how to start hunting smarter.
---
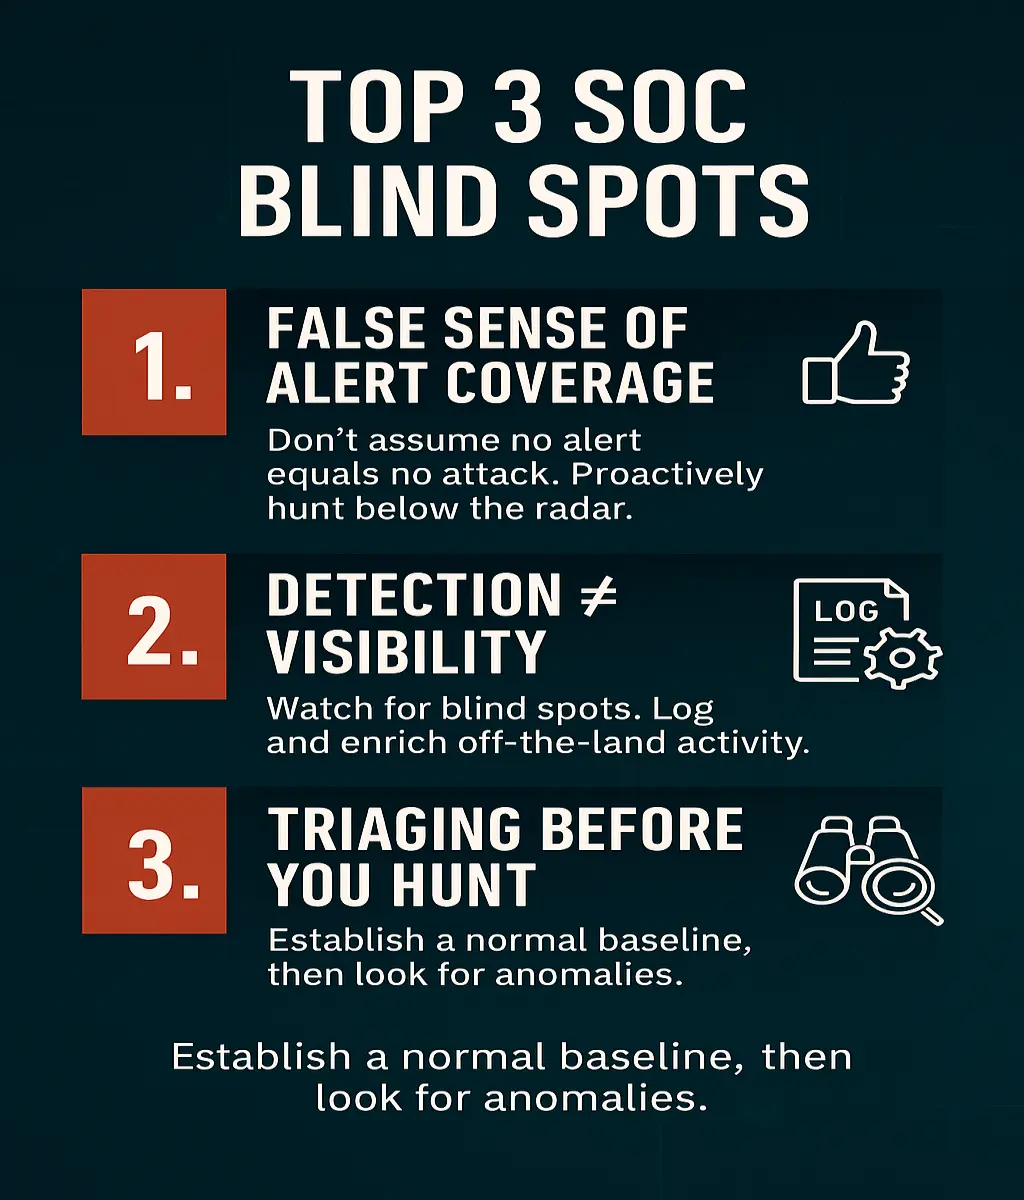
🔎 1. The False Sense of Alert Coverage
SOC teams are trained to respond to alerts. But attackers know this — so they operate beneath the alert threshold.
In one red team operation I led, we:
Used DNS tunneling with split queries
Masked C2 communications as Office365 traffic
Lived in staging environments with no EDR installed
Result: No alerts. 5 days of full access.
The SOC was waiting for the tool to “say something.”
---
🧠 2. Detection ≠ Visibility
Many teams assume that if it wasn’t flagged, it didn’t happen. But modern attacks exploit blind spots:
DNS logs not enriched or monitored
Lateral movement using living-off-the-land binaries (LOLBins)
Scheduled tasks hiding persistence
> "The logs won’t save you if your visibility is pointed the wrong way."
---
🧰 3. The Fix: Hunt First, Triage Later
In Inside the Hacker Hunter’s Toolkit, I lay out a field-tested framework for proactive hunting:
Establish baseline behavior — not just alerts
Hunt by abnormal protocol usage (e.g. DNS, RDP, SMB)
Use tools like Sigma + Arkime + Velociraptor + CyberChef
Correlate low-signal anomalies, not just high-severity alerts
> “You can’t defend what you’re not looking for.”
---
📘 Want More?
Both of my books are based on real-world cases — not theory:
📗 Inside the Hacker Hunter’s Toolkit – Tactics, workflows & tools:
👉 https://a.co/d/1Lv3plH
📘 Inside the Hacker Hunter’s Mind – Mindset, red team stories, field lessons:
👉 https://a.co/d/dWlUayj
They’re built for analysts, engineers, and leaders who want to level up and think like modern attackers.
---
#CyberSecurity #SOC #ThreatHunting #CTI #EDR #IncidentResponse #BlueTeam #HackerHunter #AhmedAwad #Nullc0d3 #InfoSec #RedTeamOps