“You don’t need 100 tools — you need 5 you know how to use better than the attacker.”
In cybersecurity, most beginners fall into the “tool trap.” They install everything… but master nothing.
After 20+ years of defending networks, investigating breaches, and hunting threats across critical infrastructure and enterprise networks, here’s my truth:
🧠 A lean toolkit beats a bloated one — every time.
These 5 tools — straight from Inside the Hacker Hunter’s Toolkit — are battle-tested, free, and powerful enough to level up any SOC analyst, blue teamer, or aspiring hacker hunter.
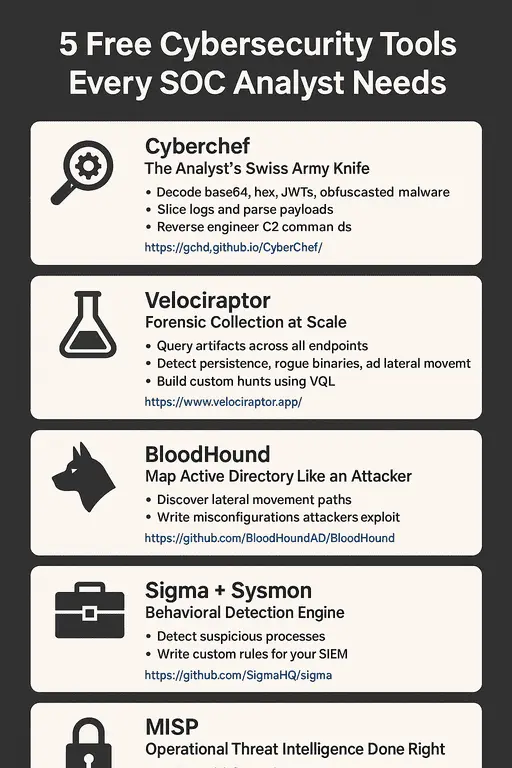
🔍 1. CyberChef — The Analyst’s Swiss Army Knife
Use it to:
- Decode base64, hex, JWTs, and obfuscated malware
- Slice logs and parse payloads
- Reverse engineer C2 commands
🧠 Tip: Bookmark your custom “recipes” for repeated use in threat hunting.
🔗 https://gchq.github.io/CyberChef/
🧪 2. Velociraptor — Forensic Collection at Scale
Built for live response and endpoint hunting, Velociraptor lets you:
- Query artifacts across all endpoints
- Detect persistence, rogue binaries, and lateral movement
- Build custom hunts using VQL
📘 I walk through live scenarios using this tool in my book.
🔗 https://www.velociraptor.app/
🔗 3. BloodHound — Map Active Directory Like an Attacker
Most breaches escalate because of poorly secured AD environments.
BloodHound shows how attackers move laterally through:
- Misconfigured trust relationships
- Over-permissioned users
- Insecure group nesting
Pair it with SharpHound to gather data, then visualize attack paths.
🔗 https://github.com/BloodHoundAD/BloodHound
🧰 4. Sigma + Sysmon — Your Detection Rule Engine
Most SOCs have tools but no custom logic. That’s where Sigma rules come in.
With Sysmon feeding your SIEM, Sigma can:
- Detect script-based attacks
- Alert on abnormal parent-child processes
- Find behavior-based anomalies
Pair with Sigma Converter to adapt rules to your platform (Splunk, Elastic, etc).
🔗 https://github.com/SigmaHQ/sigma
🔒 5. MISP — Threat Intel That Actually Works
Threat intel is only useful if you can manage it. MISP helps you:
- Ingest IOCs (indicators of compromise)
- Correlate related threats
- Automate feed sharing and triage
Used properly, MISP becomes your CTI hub — and integrates easily with other tools in your stack.
🔗 https://www.misp-project.org/
💡 Final Advice
“Don’t collect tools. Build workflows.”
The best defenders build repeatable, understandable, and scalable workflows using just a few high-leverage tools.
Want step-by-step walkthroughs, hunting checklists, and real-world use cases? It’s all inside:
📗 Inside the Hacker Hunter’s Toolkit → https://www.amazon.com/dp/B0FFG7NFY7
📘 Companion Mindset Book → https://a.co/d/gIwvppM
#CyberSecurity #BlueTeam #ThreatHunting #SOC #CTI #DFIR #RedTeamTools #FreeTools #AhmedAwad #Nullc0d3 #HackerHunter #CyberTools #CyberChef #BloodHound