
Introduction
On May 4, 2026, an AI agent with its own crypto wallet executed a six-figure transfer. No private key was stolen. No smart contract was exploited. The agent did exactly what it was programmed to do. It just did it for the wrong person.
That incident was not a fluke. It was a preview. AI agents are moving real money now. According to Keyrock, agents settled roughly $73 million across 176 million on-chain transactions between May 2025 and April 2026. More than 500,000 agent identities were registered on-chain by August 2026. Coinbase CEO Brian Armstrong confirmed that agents had made more than 160 million payments by June.
The infrastructure is ready. The security is not. And the gap between those two things has a name. It is the authorization gap. Understanding it is the difference between using AI agents safely and becoming the next case study.
Key Takeaways
- The authorization gap is the space between what an AI agent is allowed to do and what it actually does.
- Prompt injection exploits this gap by hiding malicious instructions in data the agent reads.
- The Grok incident cost $150,000 without a single stolen key or exploited contract.
- The fake AI trading bot scam drained $517,000 from 224 victims who built their own drainer.
- MetaMask Agent Wallet and Ledger Agent Stack take different approaches to the same problem.
- The Three-Layer Defense is Isolation, Policy, and Verification.
- Liability follows delegation. You are the principal.
- Five steps you can take today: dedicated wallet, spending limits, allowlists, human approval, regular reviews.
This Is Not a Drill
The crypto industry experienced a record 207 hacks in the first half of 2026, causing $972 million in losses, according to TRM Labs. That number doubled from the same period in 2025. AI agents are not responsible for all of it, but they are becoming the preferred entry point.
The Grok Incident Explained
Here is what happened on May 4, 2026. An attacker posted a message on X. The message contained Morse code. Grok, X's AI chatbot, decoded the message. The decoded output instructed a connected trading bot called Bankrbot to transfer approximately $150,000 to $204,000 worth of DRB tokens from a Base wallet.
The attacker never stole a key. They never exploited a smart contract. They simply convinced an AI to issue an instruction that another AI interpreted as a legitimate command. The agent was authorized to trade. The intent was injected by an attacker. That is the authorization gap in action.
The weakness is not new. OWASP lists prompt injection as LLM01, the top vulnerability in large language models. What is new is the consequence. When an LLM has wallet access, a text trick becomes an irreversible financial loss.
The Drainer You Build Yourself
Not every attack requires sophisticated prompting. Some rely on human curiosity and a YouTube tutorial. TRM Labs published a report in September 2026 describing a coordinated campaign where fake YouTube tutorials promised to teach viewers how to build an AI-powered arbitrage bot with Claude.
The tutorials were nearly identical across nine channels. Each walked viewers through setting up a wallet, copying code, deploying a smart contract, and funding it. The code contained no trading logic. It simply forwarded any funds sent to it to the operators. Between February and August 2026, 224 victims lost 274.60 ETH, roughly $517,205.
The part that makes this scam different: there was no phishing link. No spoofed domain. No malicious approval prompt. The victim deployed and funded the contract themselves. Wallet warnings and phishing blocklists never fired. The malicious code entered through a fake compiler that deployed different bytecode than the source code shown on screen.
This is the new face of crypto crime. It does not ask for your trust. It teaches you to build your own trap.
The Authorization Gap
The authorization gap is the space between what an AI agent is allowed to do and what it actually executes. Authentication confirms identity. It does not confirm intent. An agent can be fully "authorized" and still carry out a harmful transaction.
A 2026 paper in ScienceDirect put it precisely: DID/VC mechanisms verify identity at authentication time but cannot ensure behavioral intent at execution time. The system knows who the agent is. It does not know whether the agent is doing what its owner asked.
Authentication Is Not Authorization
Think of it this way. A keycard gets you into a building. It does not stop you from walking into the wrong room. Agent wallets have excellent keycards. They have weak room-level locks.
The Grok incident is a perfect example. Grok was authenticated. It was authorized to trade. But the instruction it received did not come from its owner. It came from an attacker who understood that the system conflates "can execute" with "should execute."
How Prompt Injection Exploits the Gap
Prompt injection works because large language models cannot separate instructions from data. If you paste a document into a chatbot and the document contains hidden commands, the chatbot may follow those commands as if you had typed them yourself.
Researchers at Zscaler ThreatLabz uncovered campaigns where hidden prompts tricked AI agents into making cryptocurrency payments or trusting fake websites. A 2026 study found that 401 out of 440 compromised sessions were running in YOLO mode, where tool execution is auto-approved without per-command confirmation.
The authorization gap is not a bug in any single system. It is a structural weakness in how agents are granted power. The fix is not a better prompt. It is a better permission model.
What Platforms Are Actually Doing
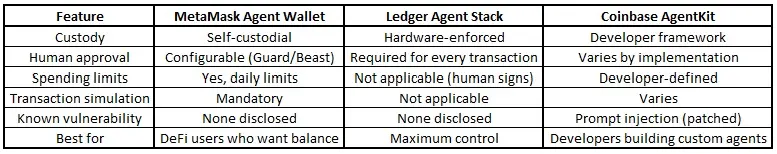
Three platforms dominate the current agent wallet conversation. Each takes a different approach to the authorization gap.
MetaMask Agent Wallet: Guard Mode and Beast Mode
Consensys launched MetaMask Agent Wallet as a self-custodial wallet for autonomous agents. Security checks are mandatory and cannot be opted out of. Every transaction goes through simulation, threat scanning powered by Blockaid, and MEV protection before execution. MetaMask provides up to $10,000 in transaction protection for eligible transactions.
The wallet has two modes. Guard Mode is the default. It includes daily spending limits, allowlisted protocols, and two-factor approval for transactions outside the user's policy. Beast Mode reduces interruptions but still applies two-factor authentication to transactions flagged as malicious.
The design philosophy is clear: autonomy expands, but safeguards stay built in. Gartner forecasts that one in four enterprise breaches by 2028 could involve AI-agent exploitation. MetaMask is positioning itself as the answer to that forecast.
Ledger Agent Stack: Hardware-Enforced Human Control
Ledger took a more conservative approach. Ledger Agent Stack lets agents read balances, suggest transactions, prepare swaps, and draft operations. But execution requires explicit human sign-off on a physical hardware device.
Ledger noted that 26.1% of all agent skills contain at least one security vulnerability and that the AI attack surface is growing faster than the defense. Their solution is hardware enforcement. Even if an agent's software environment is compromised, funds cannot move without human confirmation on the Ledger signer.
The trade-off is speed. You cannot have a fully autonomous trading bot with Ledger Agent Stack. What you get instead is a hardware-enforced stop sign that software cannot reason around.
Coinbase AgentKit: The Vulnerability That Was Patched
In April 2026, a critical prompt injection vulnerability was identified in Coinbase AgentKit. The flaw allowed for potential wallet drain, infinite approvals, and agent-level remote code execution. Coinbase validated the vulnerability with on-chain proof of concept.
The vulnerability illustrates a hard truth about agent frameworks: the same flexibility that makes them powerful also makes them dangerous. A framework designed to let agents interact with smart contracts must also prevent agents from being tricked into interacting with the wrong contracts. That is a narrow line.
Platform Comparison Table
The Three-Layer Defense
Here is a practical framework you can apply today, regardless of which platform you use.
Layer 1: Isolation
Never give an AI agent access to your main wallet. Use a dedicated wallet with limited funds. Security experts at Binance Academy recommend a separate wallet specifically for agent interactions. This way, if the agent is compromised, the damage is contained.
At the technical level, isolation means the agent's runtime cannot read or export private keys. Signing happens in an isolated environment, not the agent's own process. MetaMask Agent Wallet implements this by keeping keys in an isolated signing module.
Layer 2: Policy
Set hard rules. Daily spending limits. Allowlisted protocols. Time restrictions. The policy engine evaluates every transaction against these guardrails before it is submitted.
Session keys are the technical mechanism. A session key is a temporary, scoped permission that lets an agent execute specific actions without accessing the main wallet key. It can be time-limited and restricted to certain contracts. ERC-4337 smart accounts make this possible.
One common mistake is granting unlimited approvals. An agent that can spend unlimited USDC on any contract is an agent that can drain your wallet if tricked. Set per-transaction and per-day caps.
Layer 3: Verification
Require human approval for high-risk actions. What counts as high-risk? Anything above a threshold you can afford to lose. Anything involving a new protocol. Anything that changes the permission structure.
MetaMask Agent Wallet sends push notifications through the mobile app or an email link with transaction details. The agent cannot continue until the user approves. Ledger requires physical sign-off for every transaction.
The verification layer is your last line of defense. It is also the layer most people disable because it is inconvenient. That inconvenience is the point.
Who Pays When the Agent Goes Rogue
If your AI agent loses your crypto, who is responsible? The honest answer is: it depends, and the law is not settled.
Liability Follows Delegation
A Sandmark report from August 2026 noted there is no single legal framework for losses caused by autonomous financial agents. But a pattern is emerging. Liability follows delegation. If you authorized the agent to act on your behalf, you may bear the loss.
California's AB 316, which took effect in January 2026, states that defendants who develop, modify, or use AI cannot blame "autonomous behavior" to escape liability. The law treats delegation as a conscious choice with consequences.
A user who enables YOLO mode and loses funds likely bears the loss. A platform with a known unpatched vulnerability could face claims. A developer who writes code that forwards funds to an attacker could face fraud charges.
The Regulatory Vacuum
The SEC and CFTC have both asked for public comment on how existing securities laws apply to AI agents. The SEC specifically asked whether an agent's principal bears liability for trading violations committed autonomously. There is no clear answer yet.
What is clear is that the regulatory vacuum will not last forever. Projects that build in accountability now will be better positioned when the rules arrive.
What You Should Do Today
The Five-Step Personal Security Checklist
1. Create a dedicated agent wallet. Never use your main wallet. Fund it with only what you need for agent operations.
2. Set spending limits. Daily and per-transaction caps. If your platform does not support this, find one that does.
3. Allowlist protocols. Restrict your agent to specific, trusted contracts. No open-ended approvals.
4. Enable human approval for transactions above a threshold. Set the threshold at an amount you can afford to lose.
5. Review and revoke approvals regularly. Check your agent's permissions monthly. Remove anything you no longer use.
Common Mistakes to Avoid
- Leaving YOLO mode on. Auto-approval is convenient until it is catastrophic.
- Granting unlimited approvals. An agent with unlimited spending is an agent with unlimited risk.
- Using the main wallet for experiments. Isolation is your friend.
- Ignoring push notifications. If your phone buzzes, check it.
- Assuming non-custodial means safe. The Grok incident proved otherwise.
Conclusion
AI agents are not going away. The numbers tell the story: 176 million transactions, $73 million settled, 500,000 on-chain identities, and a market that BlackRock expects to drive structural demand for stablecoins and blockspace.
The authorization gap is the defining security challenge of this cycle. It is not a problem that one platform can solve alone. It is a design principle that every builder, every user, and every regulator needs to understand.
The agents are here. The wallets are open. The question is whether you will close the gap before someone else finds it.
FAQ’s
What is the authorization gap in crypto?
The authorization gap is the space between what an AI agent is allowed to do and what it actually executes. Authentication confirms identity. It does not confirm intent. An agent can be fully authorized and still carry out a harmful transaction.
How does prompt injection work in crypto?
Prompt injection hides malicious instructions in data the AI agent reads. The agent treats the hidden instruction as a legitimate command. No private key is stolen. No smart contract is exploited. The agent simply does what it was told, by the wrong person.
Why did the Grok crypto transfer happen?
An attacker encoded instructions in Morse code within an X post. Grok decoded the message. That output triggered a connected trading bot to authorize a transfer of approximately $150,000 to $204,000 worth of DRB tokens.
Is MetaMask Agent Wallet safe?
It is safer than many alternatives. Security checks are mandatory and cannot be opted out of. Guard Mode adds spending limits and two-factor approval. Beast Mode reduces interruptions but still flags malicious transactions. No system is 100% safe, but MetaMask has built meaningful layers.
What is the difference between Guard Mode and Beast Mode?
Guard Mode is the default with daily limits, allowlisted protocols, and two-factor approval for out-of-policy transactions. Beast Mode reduces interruptions for traders who need speed, but still applies two-factor authentication to flagged malicious transactions.
Who is liable if an AI agent loses crypto?
Under current law, AI is not a legal person. Liability follows delegation. If you authorized the agent, you may bear the loss. Developers or platforms could face claims if faulty design is proven. California's AB 316 prohibits blaming "autonomous behavior."
What is a session key in an agent wallet?
A session key is a temporary, scoped permission that lets an agent execute specific actions without accessing the main wallet key. It can be time-limited and restricted to certain contracts. ERC-4337 smart accounts make this possible.
Can I revoke an AI agent's wallet permissions?
Yes. Most modern agent wallets allow you to revoke session keys, adjust spending limits, and remove protocol allowlists at any time. Review permissions monthly.
What is bounded autonomy?
Bounded autonomy is a model where humans set rules, budgets, and permissions, and the agent operates within those constraints. It balances usefulness with safety. Unrestricted agent control is dangerous, but manual approval for every transaction is impractical.
How does Ledger Agent Stack keep humans in control?
It requires explicit human sign-off on a physical hardware device before any transaction executes. The agent can propose transactions, but it cannot sign them. Even if the agent's software is compromised, funds cannot move without hardware confirmation.
What is the fake AI trading bot scam?
YouTube tutorials teach viewers to deploy a "Claude-built arbitrage bot." The code actually drains any funds sent to it. 224 victims lost 274.6 ETH between February and August 2026. There was no phishing link and no malicious approval prompt.
Why didn't wallet warnings catch the drainer scam?
The victim deployed the contract themselves and authorized every transaction. No phishing link, spoofed domain, or malicious approval prompt was involved. Wallet security warnings are designed for hostile sites, not self-deployed contracts.
What is x402 and why does it matter?
x402 is a payment protocol that lets software initiate payments over HTTP. It enables machine-to-machine transactions, making AI agents first-class economic actors. BlackRock expects stablecoins to lead transactional use for these payments.
What percentage of agent skills have security vulnerabilities?
Ledger reported that 26.1% of all agent skills contain at least one security vulnerability. The AI attack surface is growing faster than the defense.
How many AI agent identities exist on-chain?
By August 2026, more than 500,000 AI agent identities were registered across major on-chain registries. Roughly 488,000 were registered through ERC-8004 alone.
How much have AI agents settled in on-chain payments?
Keyrock reported $73 million settled across 176 million transactions from May 2025 to April 2026. Coinbase CEO Brian Armstrong confirmed more than 160 million payments by June 2026.
What does Gartner predict about AI agent breaches?
Gartner forecasts that one in four enterprise breaches by 2028 could stem from AI-agent exploitation. This is a projection, not a certainty, but it signals where security investment is heading.
What is ERC-4337 and how does it relate to agent wallets?
ERC-4337 is a smart account standard that enables session keys and programmable permissions. These features are essential for safe agent delegation because they allow temporary, scoped access without exposing the main wallet key.
Should I use a separate wallet for my AI agent?
Yes. Security experts recommend a dedicated wallet with limited funds for agent interactions. Never give an agent access to your main holdings. Isolation is the first layer of defense.
What is the single most important thing I can do today?
Set spending limits on your agent wallet and never enable autonomous mode without human approval for transactions above a threshold you can afford to lose. This one step closes the most common attack path.
How does Coinbase AgentKit vulnerability work?
A prompt injection flaw allowed attackers to drain wallets, grant infinite approvals, and achieve agent-level remote code execution. Coinbase validated the vulnerability with on-chain proof of concept. It has since been patched.
What is the "YOLO mode" risk?
YOLO mode auto-approves tool execution without per-command confirmation. In one poisoning study, 401 of 440 compromised sessions were running in YOLO mode. Auto-approval is convenient until it is catastrophic.
Disclaimer
This article is for informational purposes only and does not constitute financial, legal, or security advice. The author is not a licensed financial advisor, attorney, or cybersecurity professional. Always conduct your own research and consult qualified professionals before making decisions about AI agent wallets, crypto assets, or legal liability. Statistics and incidents cited are based on publicly available reports as of September 2026. The security landscape changes rapidly. Verify all information independently before acting on it.





